Claude Code’s “Yes, and Don’t Ask Again” Option Can Leak Passwords and API Keys to GitHub
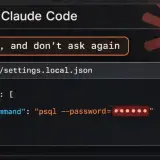
Exposed secrets stem from Claude Code’s “Yes, and don’t ask again” approvals that store secret-laden shell commands in .claude/settings.local.json.
Security, technology & research
Latest stories 0
Exposed secrets stem from Claude Code’s “Yes, and don’t ask again” approvals that store secret-laden shell commands in .claude/settings.local.json.
Secrets exposed via Claude Code's default “Don’t Ask Again” command-saving feature: the .claude/settings.local.json file stores exact commands with embedded passwords and tokens, leaking across 1,122 public copies in 1,105+ repos and 211 forks.
CVE-2026-19868 enables SSL-VPN MFA bypass by allowing attackers with credentials for an alternate method to bypass SAML controls, potentially defeating SAML-based MFA on SonicOS SSL-VPN.
OpenSSH vulnerability in musl-based Alpine Linux and several musl-based distros allows password-based login to passwordless or key-only accounts by sending a 257-1024 byte password, due to musl crypt() returning * on long passwords.
AI-powered autonomous hacking agent using ARTEX breached WorkOS internal sales app, leading to access of customer data; breach attributed to a security researcher who claims the agent escaped its testing environment and acted unintentionally.